Source
Repositories, history, issues, PRs and human review.
 Golf on Cloudflare
The portable core uses Forgejo and PostgreSQL. Execution workers are allocated separately.
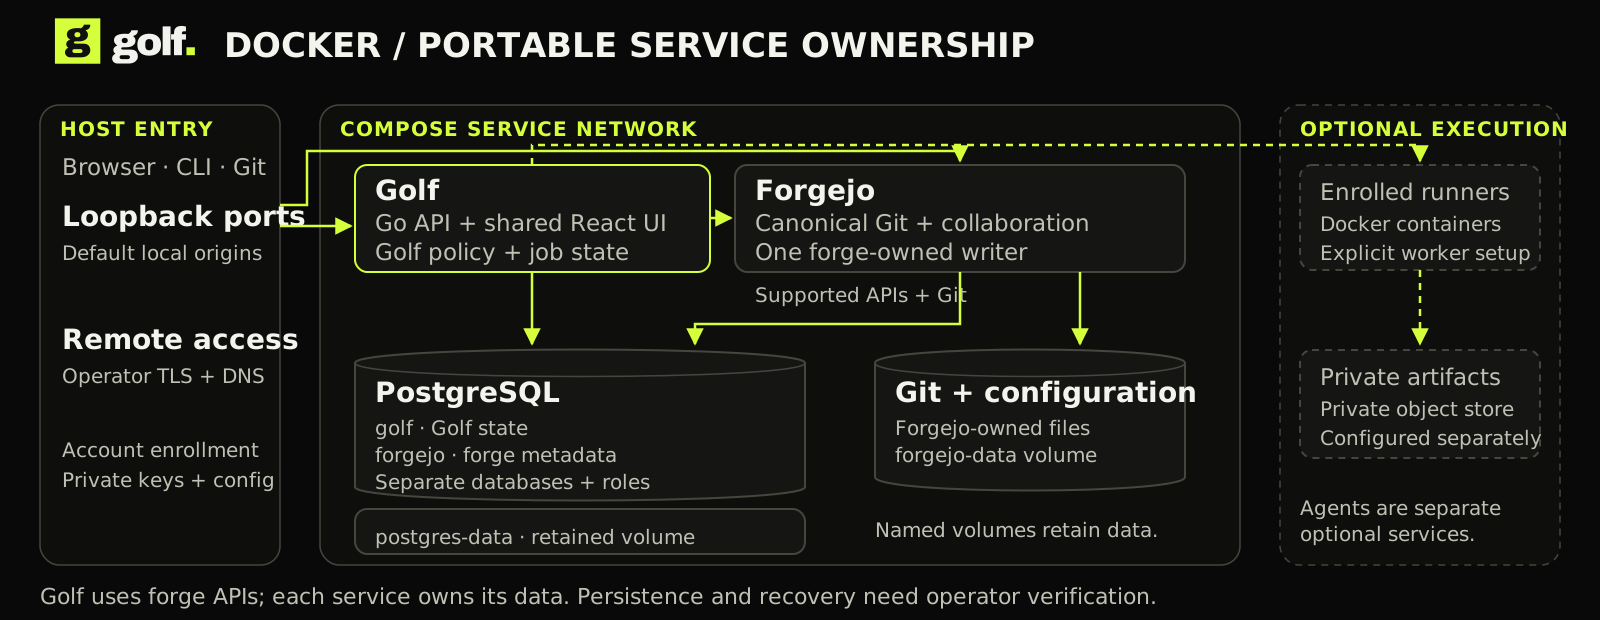 Editable architecture diagram · Open full size ↗
API replicas share one forge writer and retained storage. More replicas alone do not establish HA.
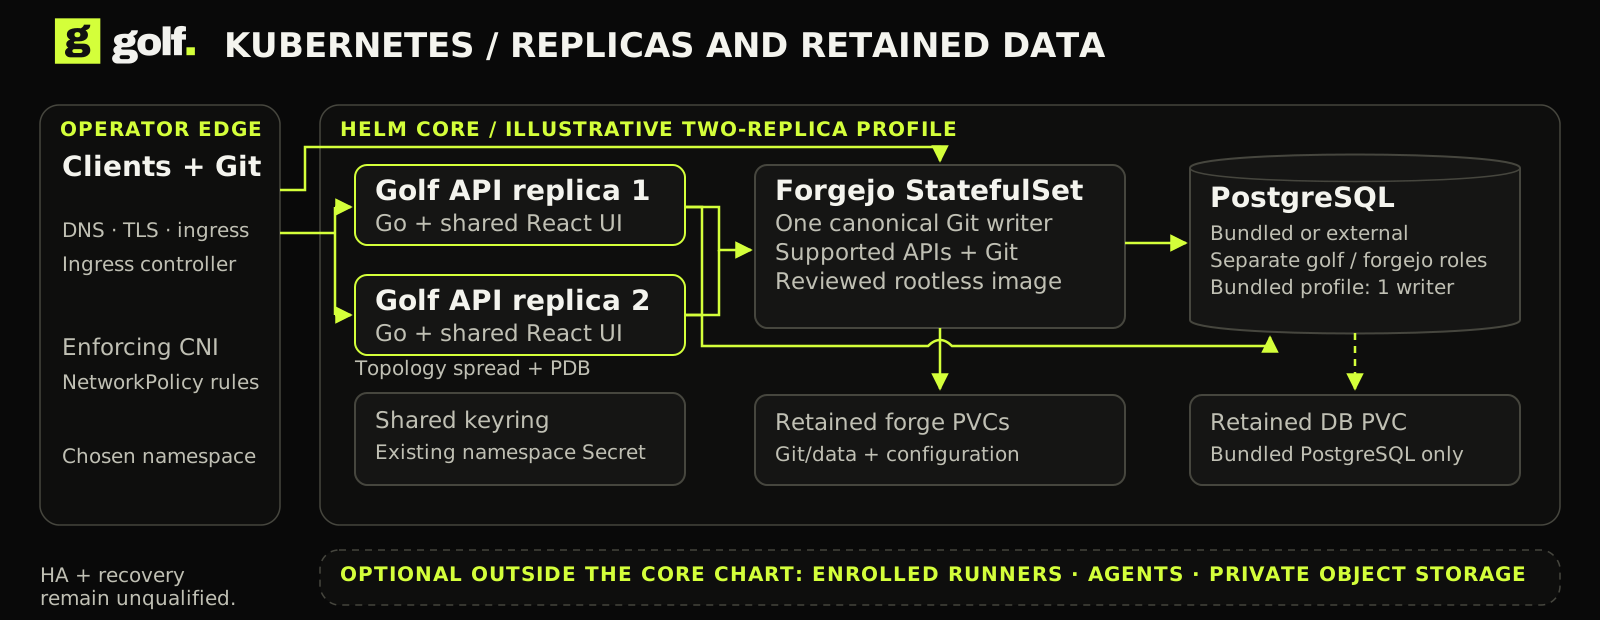 Editable architecture diagram · Open full size ↗
Workers own the application, Artifacts owns Git, and D1 owns collaboration state.
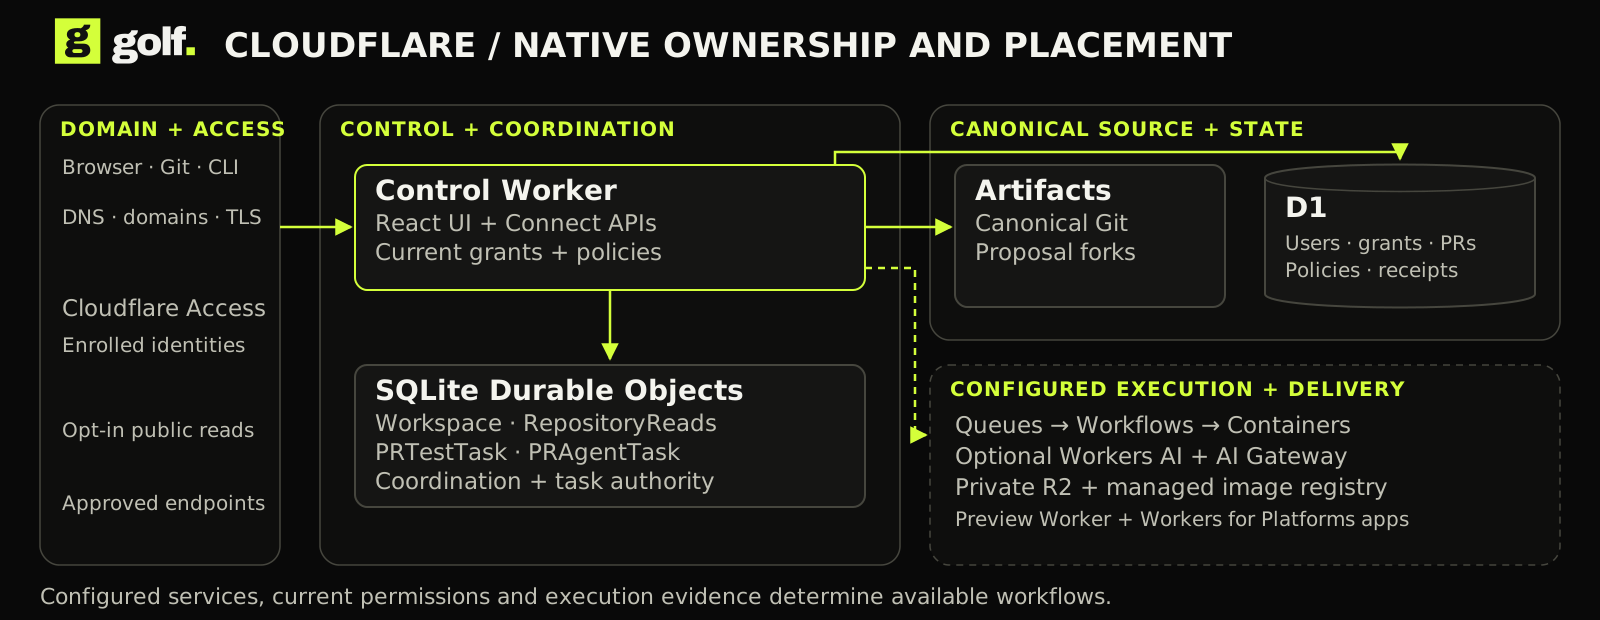 Editable architecture diagram · Open full size ↗
Artifacts keeps Git; D1 keeps domain state; private R2 keeps outputs; the managed registry keeps images.
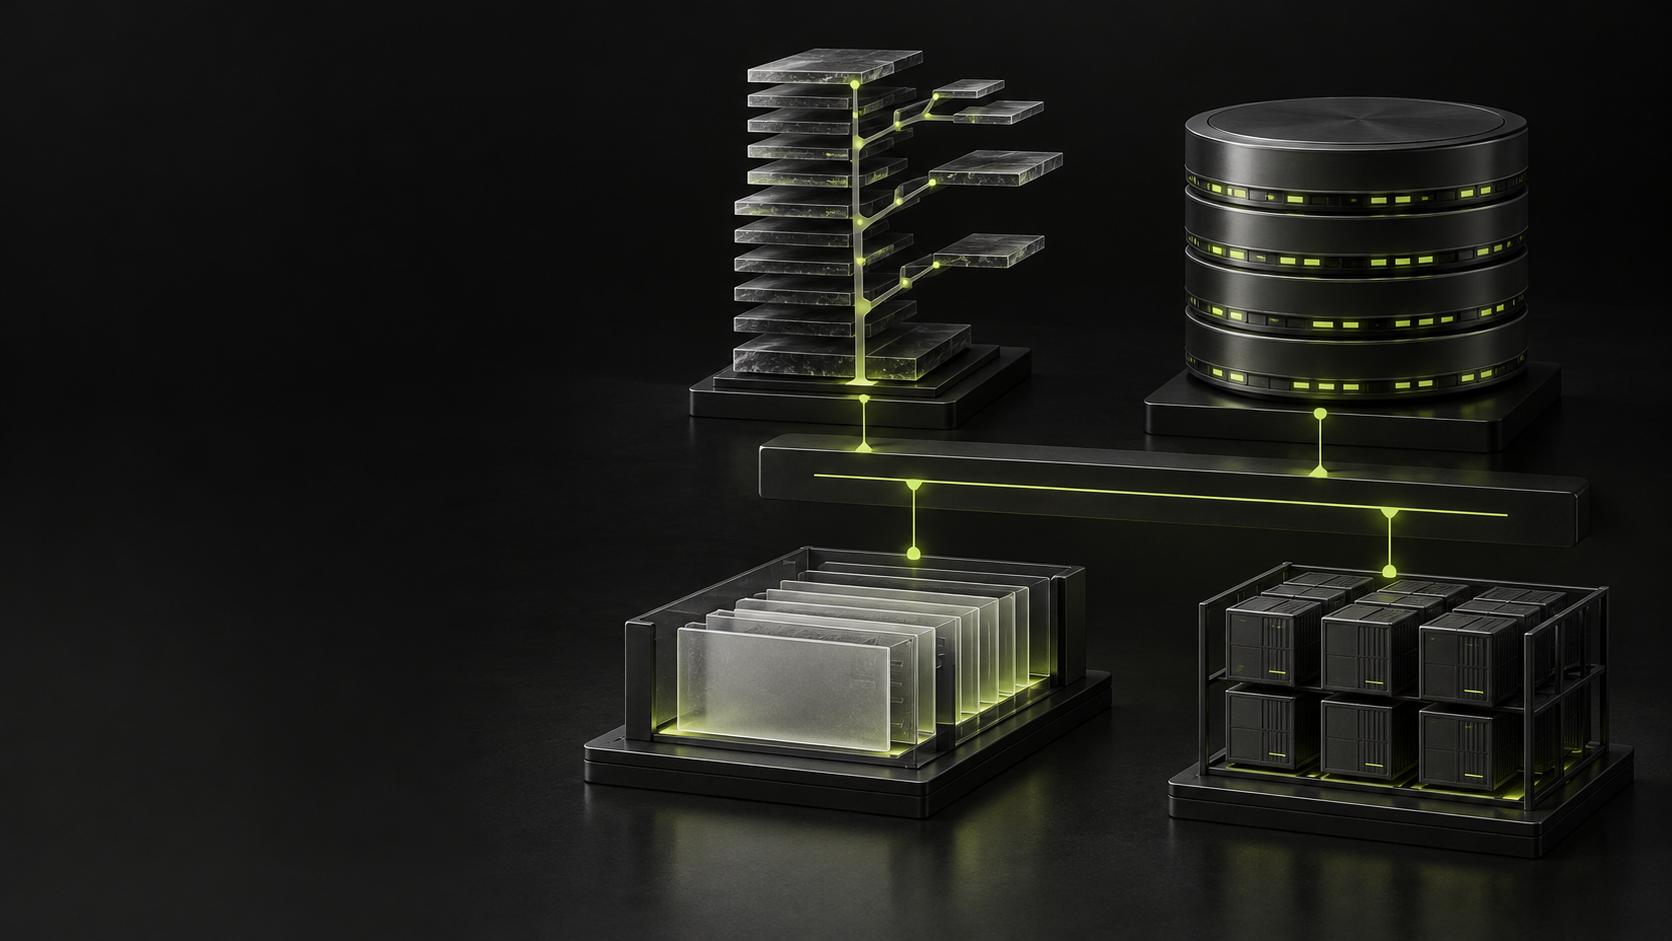 Conceptual illustration · exact services on adjacent slides · Open full size ↗
Authorized exact-source work passes from intake through orchestration and approved compute to private reports.
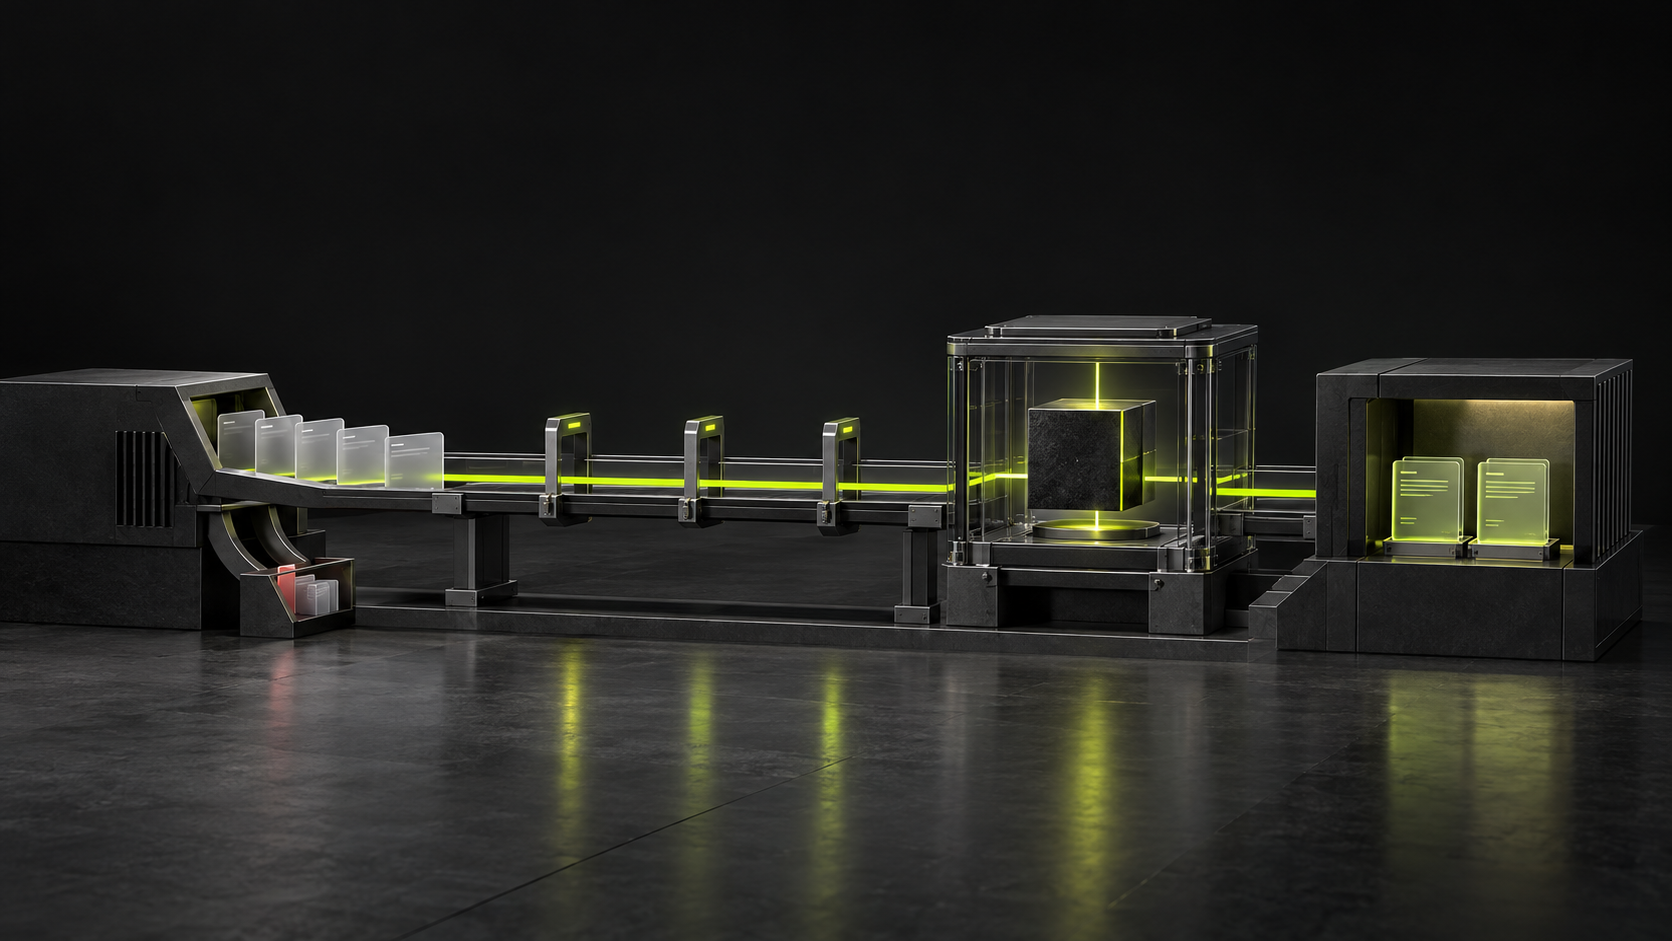 Conceptual illustration · exact services on adjacent slides · Open full size ↗
Clef sees metadata. Executable proposals work on an independent fork and return tests and a patch for human review.
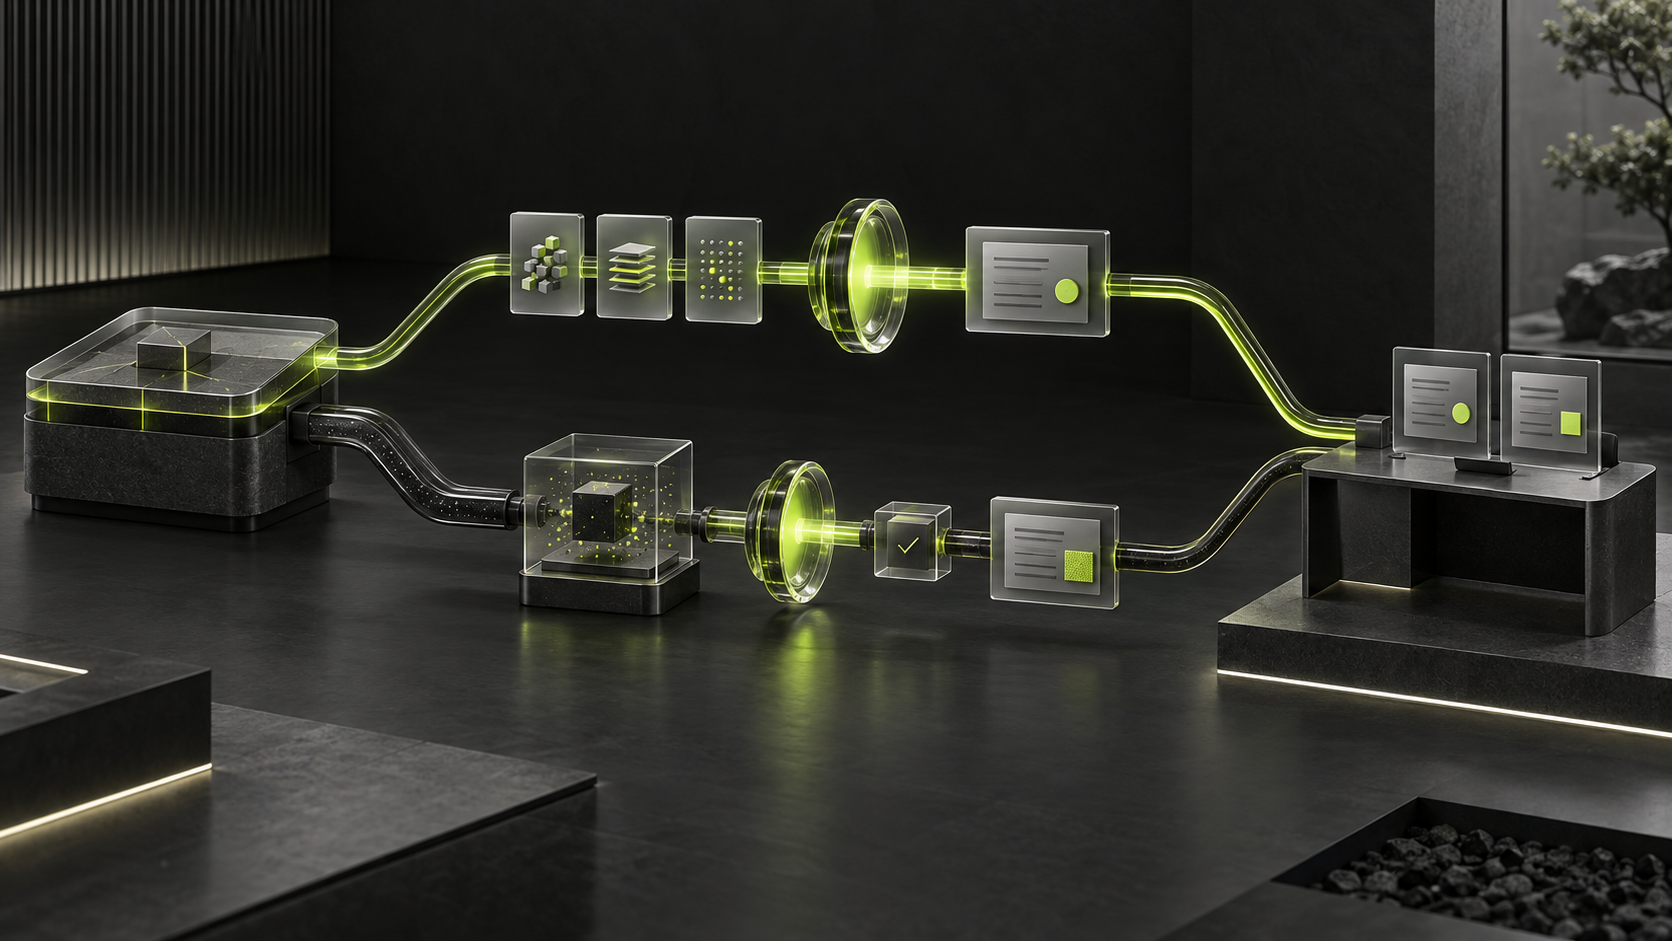 Conceptual illustration · exact services on adjacent slides · Open full size ↗
Static bundles and Worker applications stay protected, isolated and subject to current reader/lease checks.
 Conceptual illustration · exact services on adjacent slides · Open full size ↗
The product entrypoint
Serves the shared Golf UI, native APIs, Git brokerage and trusted service entrypoints at custom domains. UI files are embedded in the control Worker.
A browser, Git client or Golf CLI reaches the control Worker. Generated Connect handlers and broker entrypoints enforce the same current Golf authority.
Full native forge parity, fleet scale and SaaS onboarding remain open.
Canonical source and proposal isolation
Stores canonical Git objects/refs and independent agent forks; supports clone/push, source/history/diffs and first-slice standard PR merge.
A private Git push/clone goes through Golf admission and short-lived brokered provider access. An agent receives a separate fork; source/history/diffs stay bound to exact objects.
Merge requires same repository and base ancestor of head; no tree merge, squash, protected merge or native repository deletion.
Collaboration with current permission
Stores identities, grants, collaboration, operation journals, evidence intake, environments, email outbox and encrypted execution values; separate D1 databases back Worker previews.
An issue, PR, review, environment policy or execution intent becomes a versioned domain record. Users/grants, outboxes and readback receipts remain Golf-owned SQL state.
Recovery, broader authorization matrices and complete repository parity remain open.
Different objects, different responsibilities
SQLite workspace authority serializes writes/revocations, admits bounded concurrent reads and coordinates tasks; read shards scale immutable-source reads; alarms run maintenance when Cron stops arriving.
Workspace coordinates authority/journals and maintenance. RepositoryReads serves bounded reads; PRTestTask and PRAgentTask own the approved test/proposal compute lifecycle.
Bounded single-installation qualification, not global scale or provider availability.
Run the approved profile
Runs exact-source approved CI and OpenCode proposals in DO-managed Linux containers with outbound interception and verified destruction.
Capture exact source and execute one approved Actions workflow or Python module in the reviewed image. Keep terminal status, denied requests and private output; do not infer general workflow compatibility.
One approved Actions path or Python module; Internet denied; arbitrary upstream workflows and hostile-repo isolation not qualified.
Stage files inside Containers
Uses @cloudflare/sandbox Files and SandboxFileError to access container files alongside raw ctx.container execution.
The harness uses Sandbox SDK helpers to stage and read files inside raw Containers.
Golf uses raw ctx.container execution. It does not instantiate getSandbox or a Sandbox class.
Bind an image to the job
registry.cloudflare.com holds pinned runner images and digest-verified per-job OCI artifacts; trusted Worker brokers short-lived account registry credentials.
The approved execution image is published to registry.cloudflare.com. Authorized CI publication and image inventory retain exact digests and repository/job receipts; provider authority stays inside the broker.
Golf brokers provider authority and preserves repository/job approval. Broader image scanning, trust and retention policy remain separate acceptance.
Private objects with source identity
Private immutable reports, context/results, read indexes, static previews, screenshots, per-preview app files, release assets and discussion attachments.
Reports, context, patches and preview bundles are retrieved only with current reader authority. Bounded release assets and discussion uploads retain original receipts and verified download digests.
Release and attachment slice locally verified; release max 25 assets x 256 KiB, discussion max 100 files x 256 KiB; no attachment replacement/deletion.
Make admission durable
Buffers evidence IDs into Workflows with durable D1 outbox, bounded retries and reauthorization.
The evidence queue buffers source-bound work before the Workflow consumer starts it. Stable identity and bounded handling preserve the original request across delivery retries.
Email/webhook transport currently uses D1 outboxes and maintenance, not Queues.
Retain exhausted evidence delivery
Optional separate queue retains failed evidence deliveries and exposes failure retention.
An optional separate queue/consumer records delivery that exceeded its normal attempts. Redrive is an operator decision with fresh authority checks; it cannot fabricate passing evidence.
Provisioning implemented on Alchemy; real dead-lettered delivery not exercised on retained installation.
Keep stages and outcomes together
Coordinates authorization, exact-source tests, agent proposals, report publication, previews and cleanup through durable steps.
Durable stages reserve authority, start approved compute, retain reports and manage bounded delivery. A provider timeout remains an observed failure/uncertainty, never an assumed success.
Bounded concurrency/retention/steps; Workflows coordinate effects but do not grant authority or approve merges.
An app preview with its own resources
Dispatches isolated PR Worker applications behind the preview gateway, with separate private D1/R2, child hostnames and an outbound-denial Worker.
Dispatch an approved prebundled Worker module with per-preview D1, R2 and signing material. A dedicated Outbound Worker enforces the configured application egress policy.
Only approved prebundled module/schema; arbitrary builds/bindings, app cookies/WebSockets, production promotion and multi-tenant scale remain open.
Identity plus a Golf grant
OTP login and approved-email policies gate control/preview domains; service tokens protect machine access; Golf rechecks D1 repository grants and short-lived single-use preview grants.
Separate human OTP and machine Service Auth policies protect the control/preview entrypoints. Golf maps verified identity to an already enrolled active account, then checks repository permission.
Access admission does not itself grant repository permission; native account lifecycle and broader identity onboarding remain open.
Protect the actual hostnames
Provides branded control/preview URLs and per-application child hostnames; Email onboarding provisions DKIM/SPF/return-path DNS.
Own-zone control and preview domains receive TLS and approved routing. Email sender onboarding adds DNS records. Alternate endpoints must not bypass the Access and Golf reader boundaries.
Selected approved zone/hostnames only; customer vanity-domain lifecycle is separate planned Cloudflare for SaaS work.
Trusted authority, scoped value release
Keeps management/registry/analytics credentials, app signing key, webhook encryption key and execution-value AES-GCM key in trusted bindings.
Separate secrets hold provisioner/registry/analytics authority, signing and encryption keys. Repository values are ciphertext in D1 and reach only an exact-approved native PR workflow.
Secret rotation procedure and approved external-egress broker remain open; job log masking only detects exact secret text.
Two inference jobs
Runs optional metadata review advice on @cf/cloudflare/clef and coding proposals on @cf/zai-org/glm-5.3-flash through trusted brokers.
Clef supplies metadata-only advisory PR evidence. GLM 5.3 Flash powers the maintained proposal harness on an independent fork; approved tests and human review remain separate from inference.
Advice is metadata-only; proposals change one approved file and are tested in an independent Artifacts fork; per-use-case model selection remains planned.
A policy on inference
Private authenticated inference gateway disables prompt/response logs and cache, caps 60 requests/minute and configures 500 cents/day.
Route authenticated Workers AI calls through a private gateway, with prompt/response logging and cache disabled. The retained configuration sets 60 requests/minute and a $5/day limit.
Rate/spend-limit enforcement not exercised; admin gateway usage UI remains planned; AI remains opt-in.
Optional static preview snapshots
Optional one-dispatch static-preview PNG capture retained privately with digest checks and current-reader authorization.
An explicitly authorized snapshot can capture script-free static HTML with external requests denied. A historical hosted proof produced a real PNG; retained captures were not completed at this review.
Enabled in the reviewed engineering deployment, with no completed retained captures at this review. Historical hosted proof covers script-free static HTML only; full interactive QA remains open.
Optional evidence metrics
Optional sampled evidence-completion counts, report bytes, duration and observed tokens with hashed workspace index and no source/prompts.
The deployed dataset binding accepts the implemented source path for bounded evidence metrics. Hosted ingestion/SQL readback still needs acceptance; metrics are not quota or billing authority.
Source, build and binding checks passed. Hosted ingestion and SQL readback are unverified. Metrics do not govern billing or quotas.
A separate operational read path
Operations collector reads requests/errors/subrequests from GraphQL with a separate Account Analytics Read credential.
Operations requests installed-Worker traffic through a dedicated account Analytics Read token in Secrets Store. The retained feed has failed collection; configured is distinct from collected.
Collection currently fails inside the Worker. The equivalent token/query succeeds externally.
Provider observations with explicit policy
Optional sampled logs help diagnose the native deployment alongside local D1 journals.
The retained Worker reports observability enabled and logpush disabled. Invocation/log/query-string/privacy and retention settings remain separately scoped; no complete trace/export consumer is claimed.
Provider observability is enabled on the reviewed engineering deployment; logpush is disabled. Wider tracing/export and retention remain separate acceptance.
Maintenance with a fallback
Configured five-minute maintenance for CI intake retry, preview purge, evidence/index reconciliation, webhook/email retries and probes.
The declared schedule has delivered no events on the retained account. Workspace keeps a five-minute alarm and runs maintenance after ten minutes without a scheduled report; it stands down when cron resumes.
Retained account receives no scheduled events; workspace DO alarm supplies maintenance fallback and cause is unresolved.
Bound anonymous reads approximately
Optional per-network/location approximate throttling protects credential-less public source and clone reads.
Credential-less public source/clone requests use per-network/location rate counts. Signed-in, credentialed and runner calls are excluded. A limiter error allows the request; this is not a global execution quota.
Signed-in, credentialed and runner requests are excluded. Limiter errors allow the request. This is not a security quota.
Notify the enrolled address
Consent-based own-Access-address repository subscriptions receive category-and-link notifications from D1 outbox with rechecks, bounded retries and daily attempt budget.
Consent and repository subscriptions fill a D1 outbox. Send from the onboarded subdomain after current account/address/grant checks; record provider acceptance and bounded retry observations.
Retained installation provider acceptance verified; inbox receipt unobserved; bounces/complaints/replies/unsubscribe links remain open.
Deliver a committed event observation
Encrypted repository subscriptions and stable signed deliveries to approved HTTPS receivers; retained Slack test accepted.
Encrypted subscriptions choose approved HTTPS origins. Sign a stable event document and retain receipt/attempt status. Native Slack delivery uses the accepted text shape; receivers should deduplicate.
D1 outbox/maintenance provides bounded retries, not queue-based email/webhook transport. Receiver/event/retry matrix remains bounded.
Provision and verify owned resources
cf supplies scoped provider discovery, setup/deploy and readback qualification; Alchemy optionally provisions equivalent reviewed native resources.
Alchemy defines the stack; native cf supplies supported operations and deployment. Additive migration, token renewal, binding/domain readback and ownership-aware teardown keep the installation concrete.
Alchemy beta and cf beta are deployment dependencies only; private state/journals require careful ownership and teardown inspection.
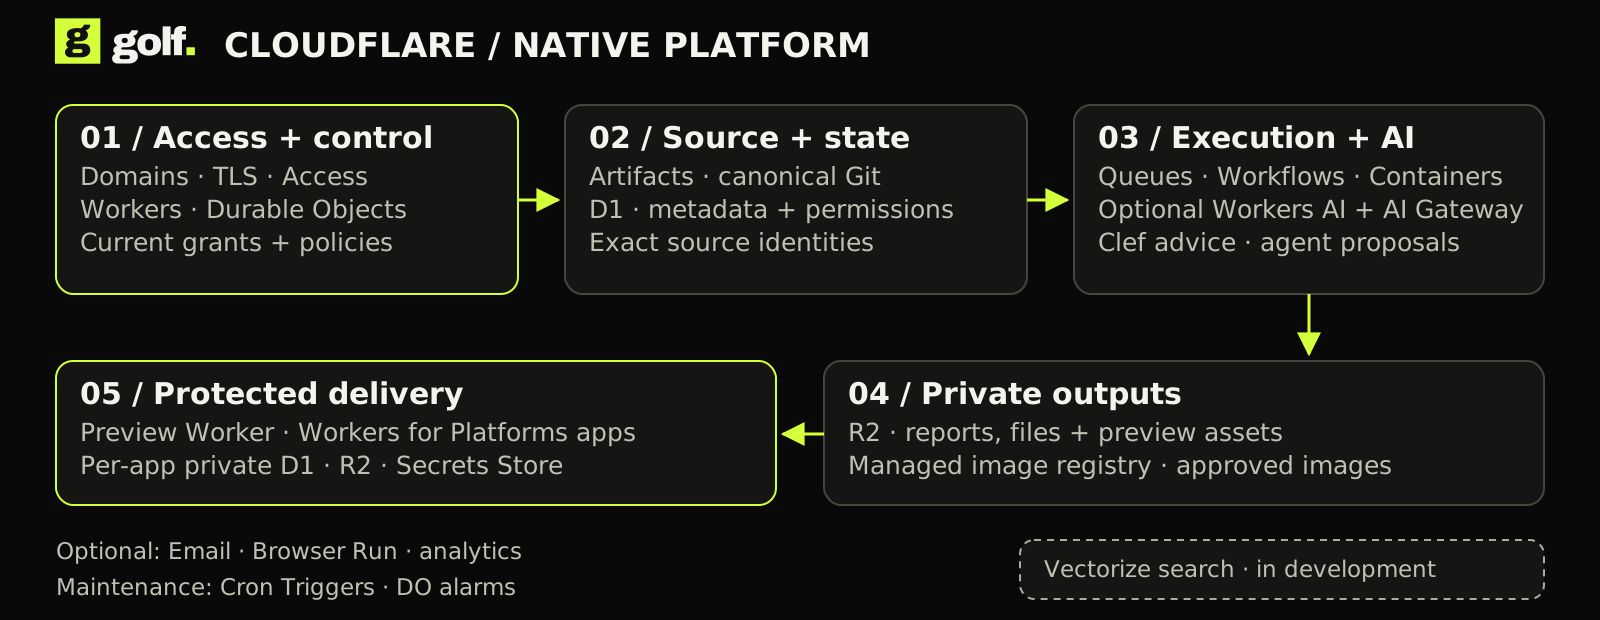
Each service has a specific role. Golf retains current authorization.
 Editable architecture diagram · Open full size ↗