Source
Repositories, history, issues, PRs and human review.
A practical source-to-preview workflow.
Golf connects Git, collaboration, executable evidence, optional proposals and protected previews.
Repositories, history, issues, PRs and human review.
Approved exact-source tests, reports and proposals.
Protected static and bounded Worker app previews.
Follow one exact change through the workspace.
Select the repository, branch and exact commit.
Open an issue or same-repository PR and request review.
Run an authorized profile and inspect the terminal report.
Publish an allowed protected preview and inspect the result.
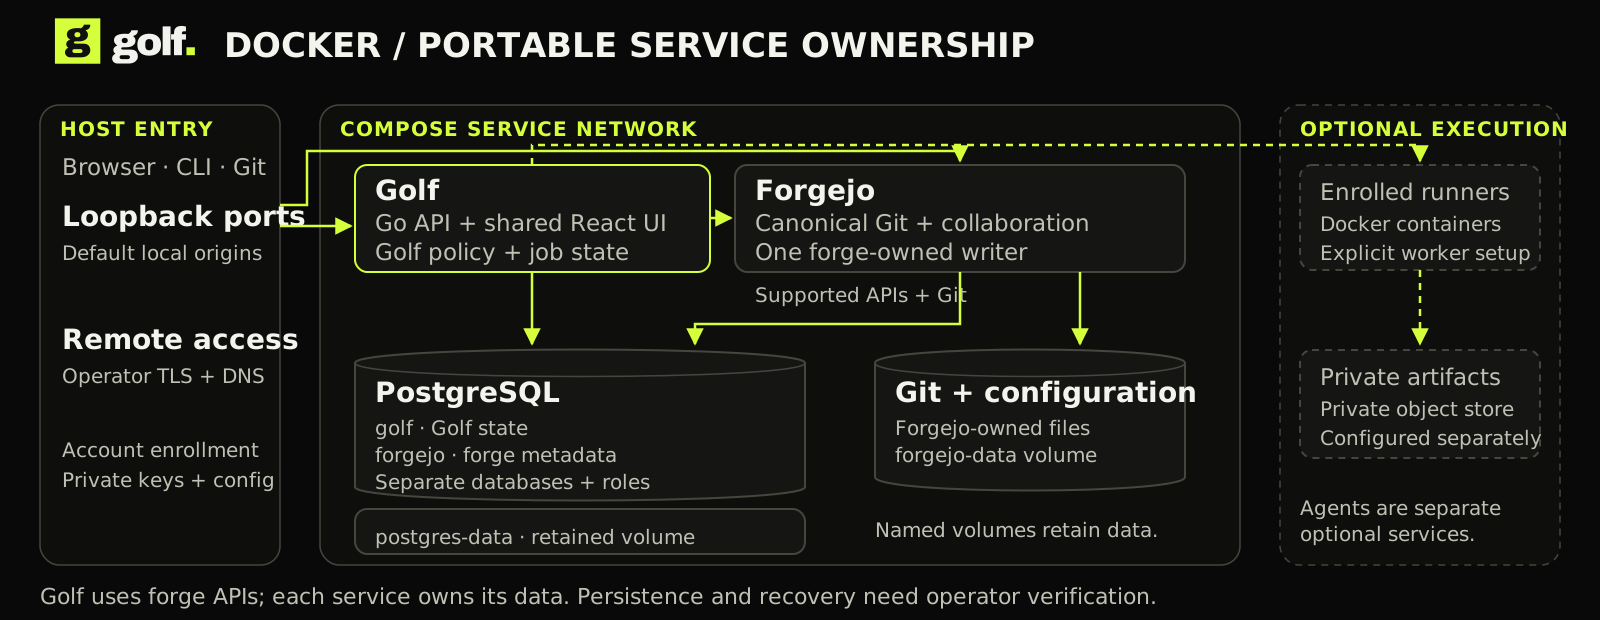
Run a complete developer core on your machine or owned Docker infrastructure.
Golf React/Go, Forgejo and independent PostgreSQL databases/roles. Private configuration and persistent volumes survive ordinary restarts.
Initialize private environment files, start Compose, check /readyz, then enroll a mapped Golf account. Optional Docker workers, agents and object storage require their own setup.
Image/version choices, HTTPS beyond loopback, secrets, data volumes and coordinated recovery. No Cloudflare or AI account is needed for core work.
The portable core uses Forgejo and PostgreSQL. Execution workers are allocated separately.
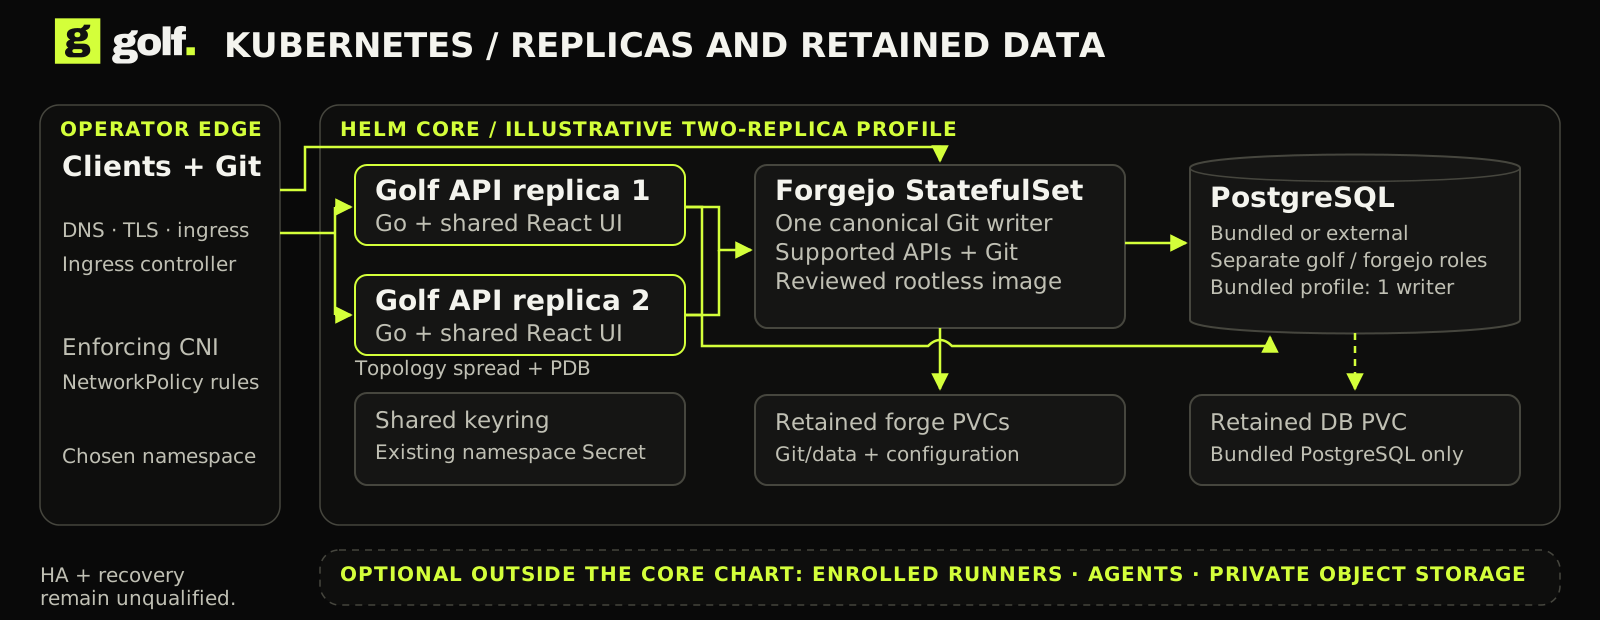
Golf’s Helm chart packages the portable core and makes its operating boundaries explicit.
Golf replicas, one Forgejo writer, optional PostgreSQL, resources/probes, retained claims, non-root isolation and default-deny policies.
Upgrade identity/endpoint fences, API hostname spread and multi-replica disruption budget, graceful drain, private database CA mounts and explicit DNS/egress peers.
Built image, existing credential/certificate Secrets, enforcing CNI, storage, ingress/TLS/DNS and a tested recovery procedure. Runners and agent services remain separate.
API replicas share one forge writer and retained storage. More replicas alone do not establish HA.
Artifacts, D1 and Workers replace origin-backed forge infrastructure on this track.
Shared UI/Connect services in Workers; Artifacts canonical Git; D1 collaboration/policy; SQLite Durable Objects coordinating reads and execution.
Queues, Workflows and Containers produce evidence. Private R2, managed registry and protected Worker apps retain outputs. Optional AI, browser snapshots, email and operations add focused consumers.
Alchemy or the native cf recipe provisions owned resources under the selected account, Access identity, domains, images and permissions. Verify actual schema, grants, readback and cleanup.
Workers own the application, Artifacts owns Git, and D1 owns collaboration state.
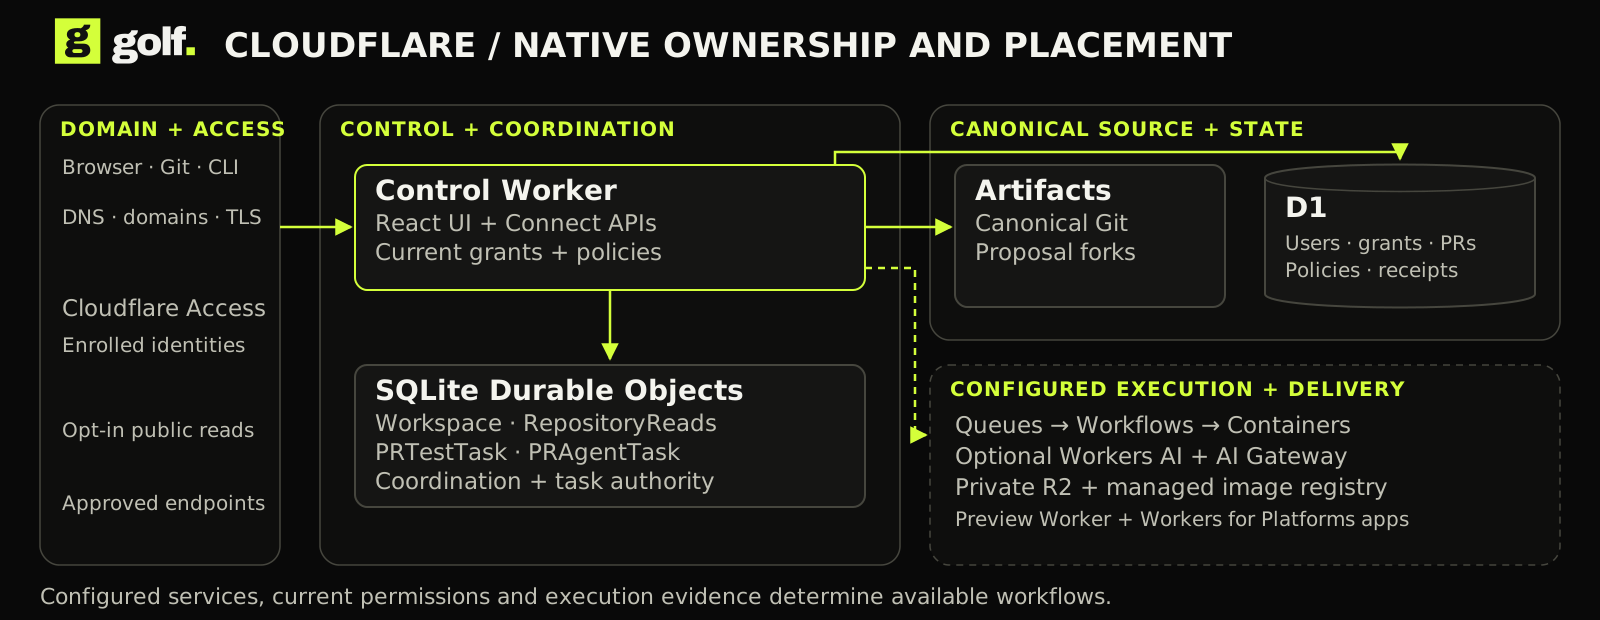
Each service has a specific role. Golf retains current authorization.
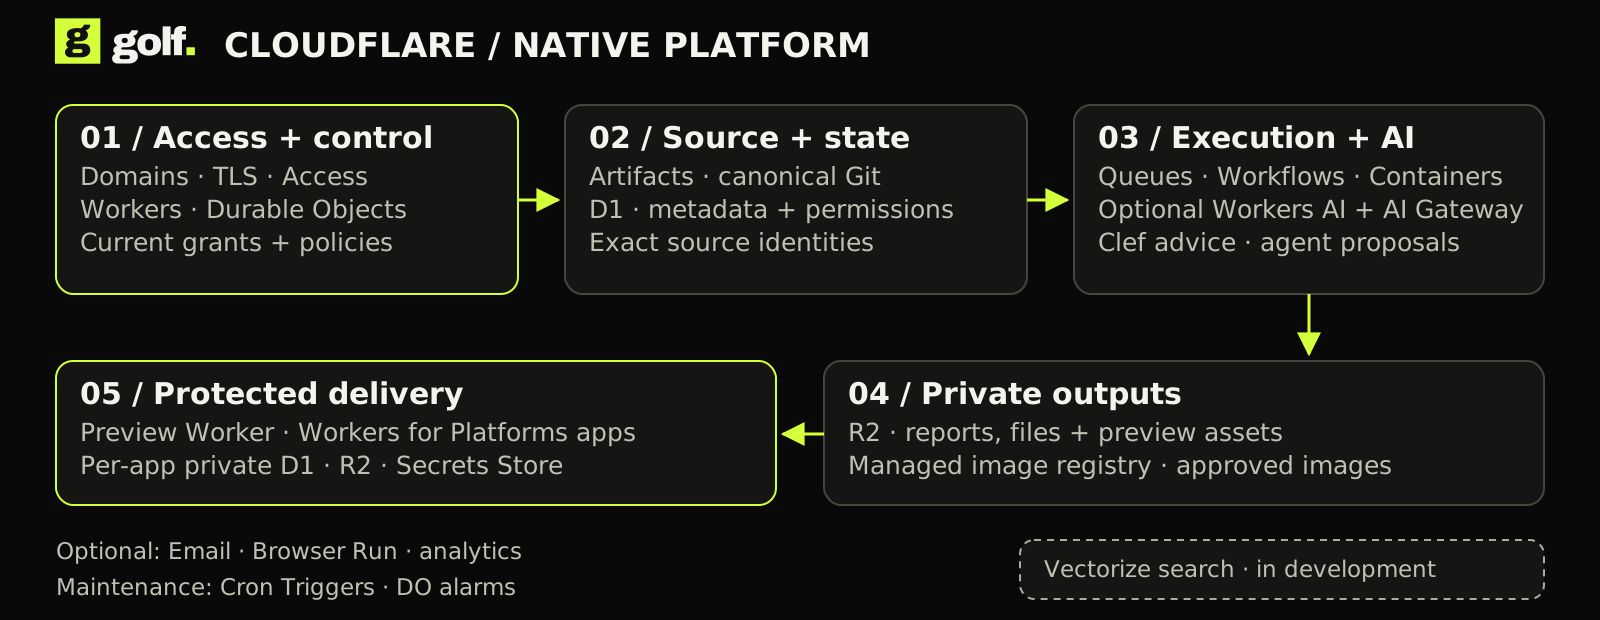
The control plane is native to Cloudflare.
Shared React UI, generated Connect APIs, Git brokerage and trusted service entrypoints.
Canonical Git objects and refs, source/history and independent proposal forks.
Accounts, repository grants, collaboration, policy, operation receipts and job records.
Workspace and RepositoryReads coordination; PRTestTask and PRAgentTask execution authority.
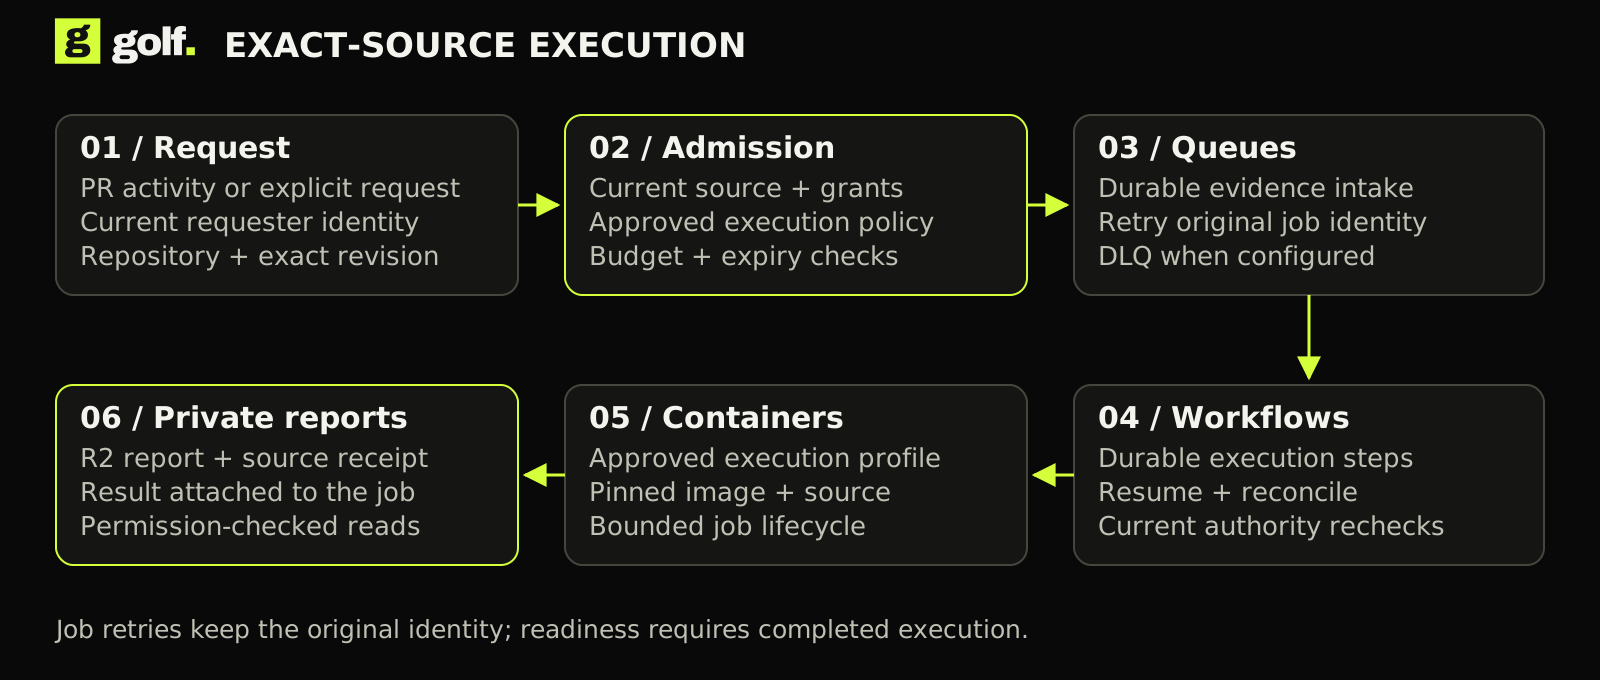
Run a selected exact-source profile and retain what actually happened.
Buffer evidence admission; optional DLQ retains exhausted messages for deliberate recovery.
Retain staged orchestration and outcomes; never grant repository authority.
Approved images execute checks and proposals with bounded source and network access.
File staging inside raw Containers. A separate general Sandbox runtime is not implied.
From authorized admission to retained private evidence.
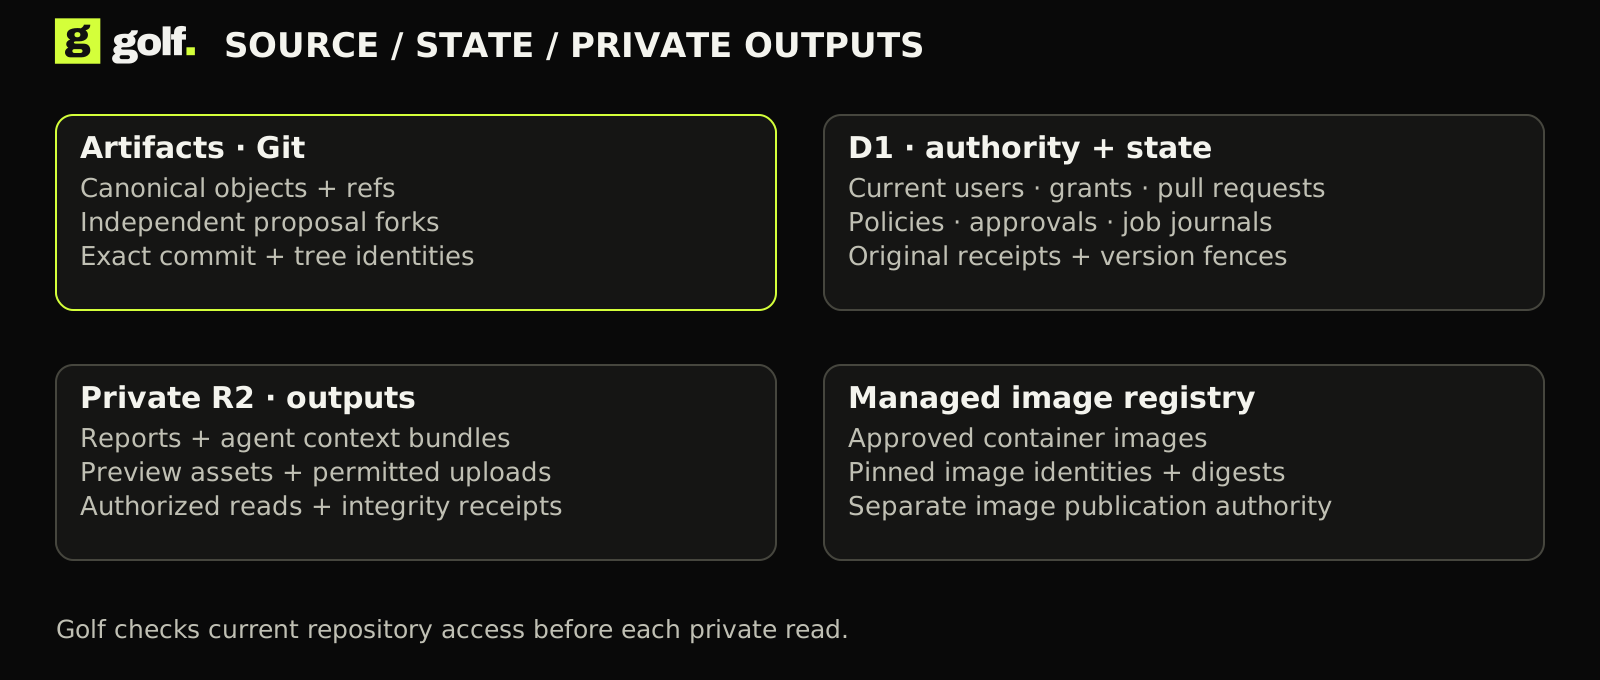
Use different storage for different responsibilities.
Git history and proposal forks, with current reader/writer checks.
Reports, agent context, preview bundles, release assets and discussion attachments.
Approved execution images and CI publication on registry.cloudflare.com; Golf retains digest receipts.
Broker authority, signing material and encryption keys; never browser-held provider secrets.
Give each kind of data the right home.
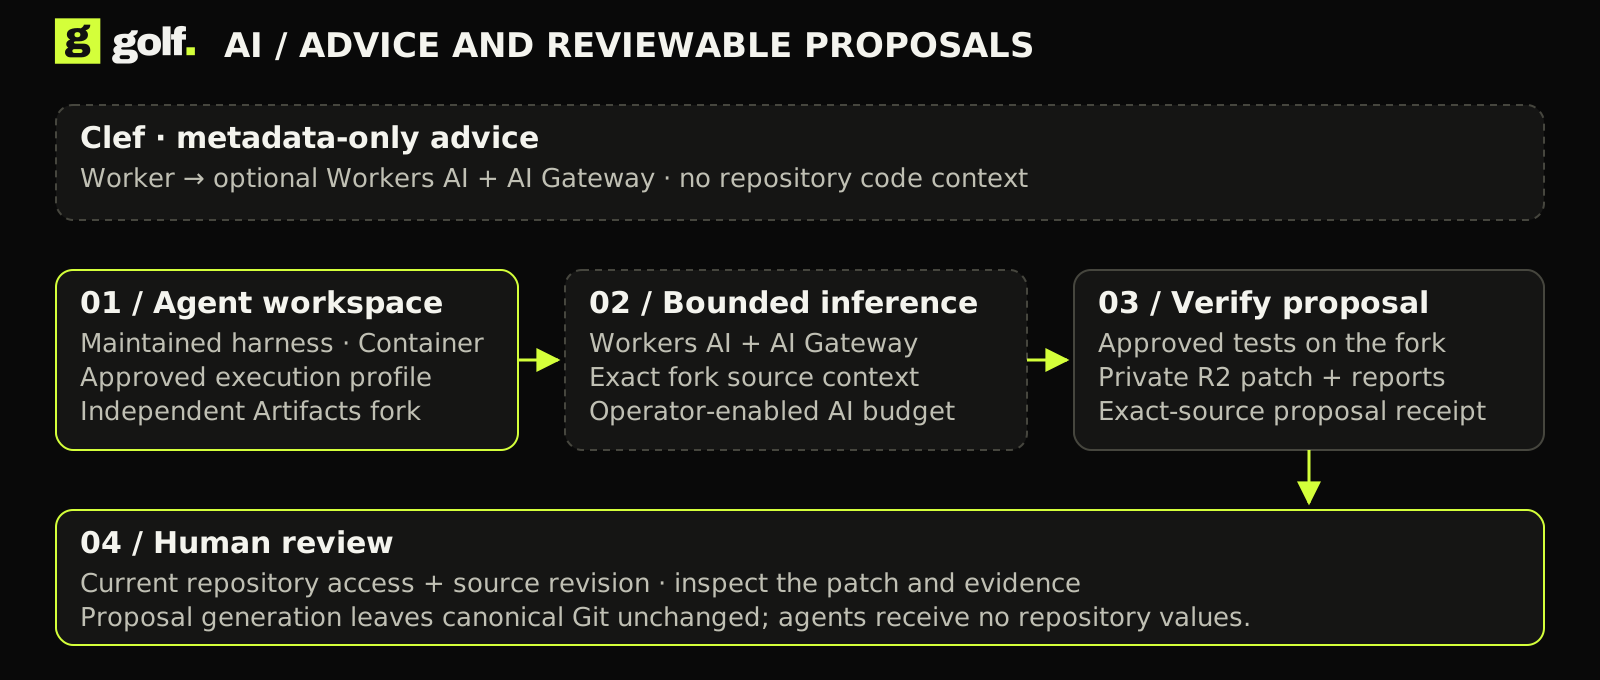
Optional inference serves a specific workflow.
Metadata-only PR reasoning through Workers AI. Advisory evidence; no approval or merge authority.
Maintained harness in an independent Artifacts fork. Approved file changes, tests and private reports.
Authenticated inference; logs and cache disabled. Configured 60/min and $5/day limits.
Clef advice and separately tested proposals serve different jobs.
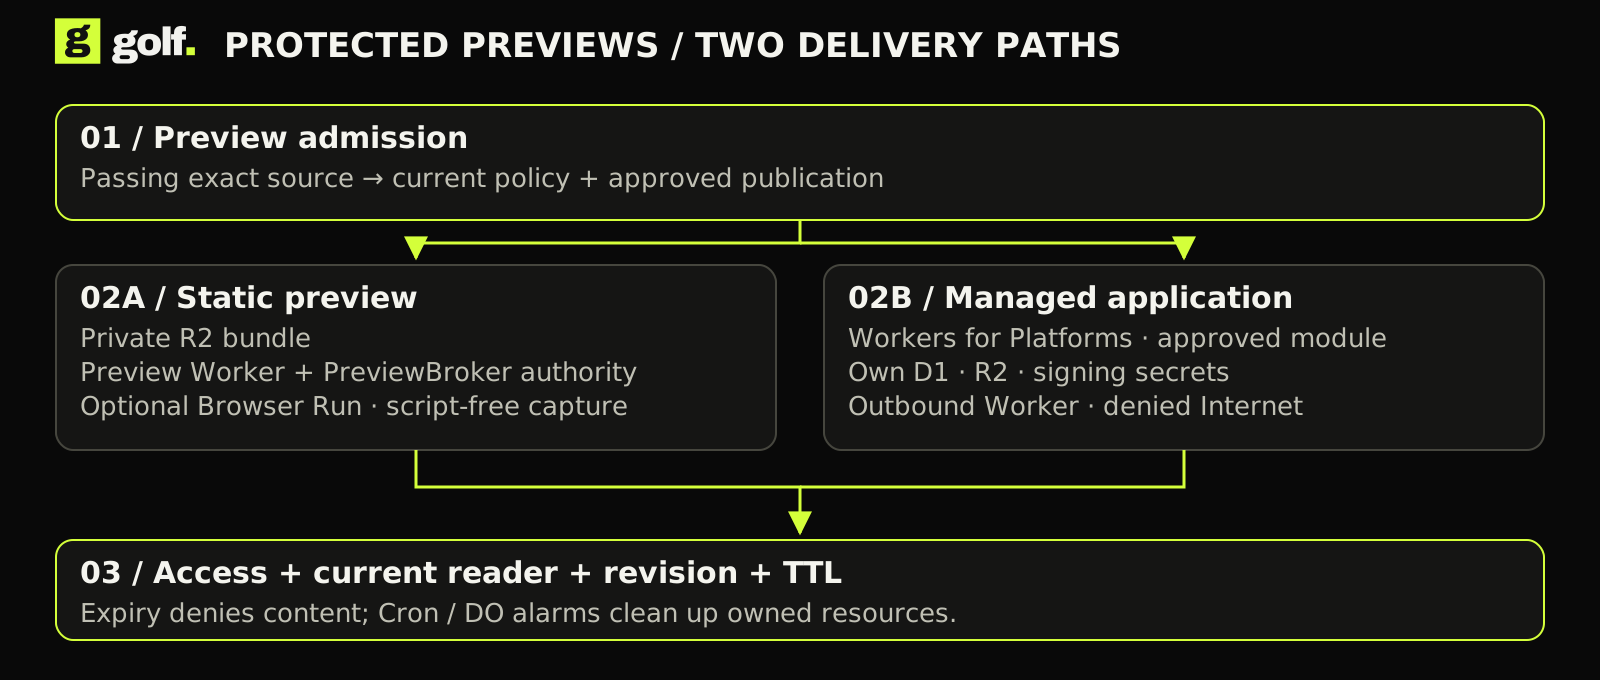
Temporary, source-bound previews keep production separate.
Broker the exact static bundle with current reader checks and expiry.
Dispatch approved modules with private per-preview D1/R2 and signing material.
Enforce the managed app egress policy instead of handing apps unrestricted Internet access.
Optional script-free static HTML snapshots. Full interactive application QA remains open.
Protect readers and isolate the application’s data and network access.
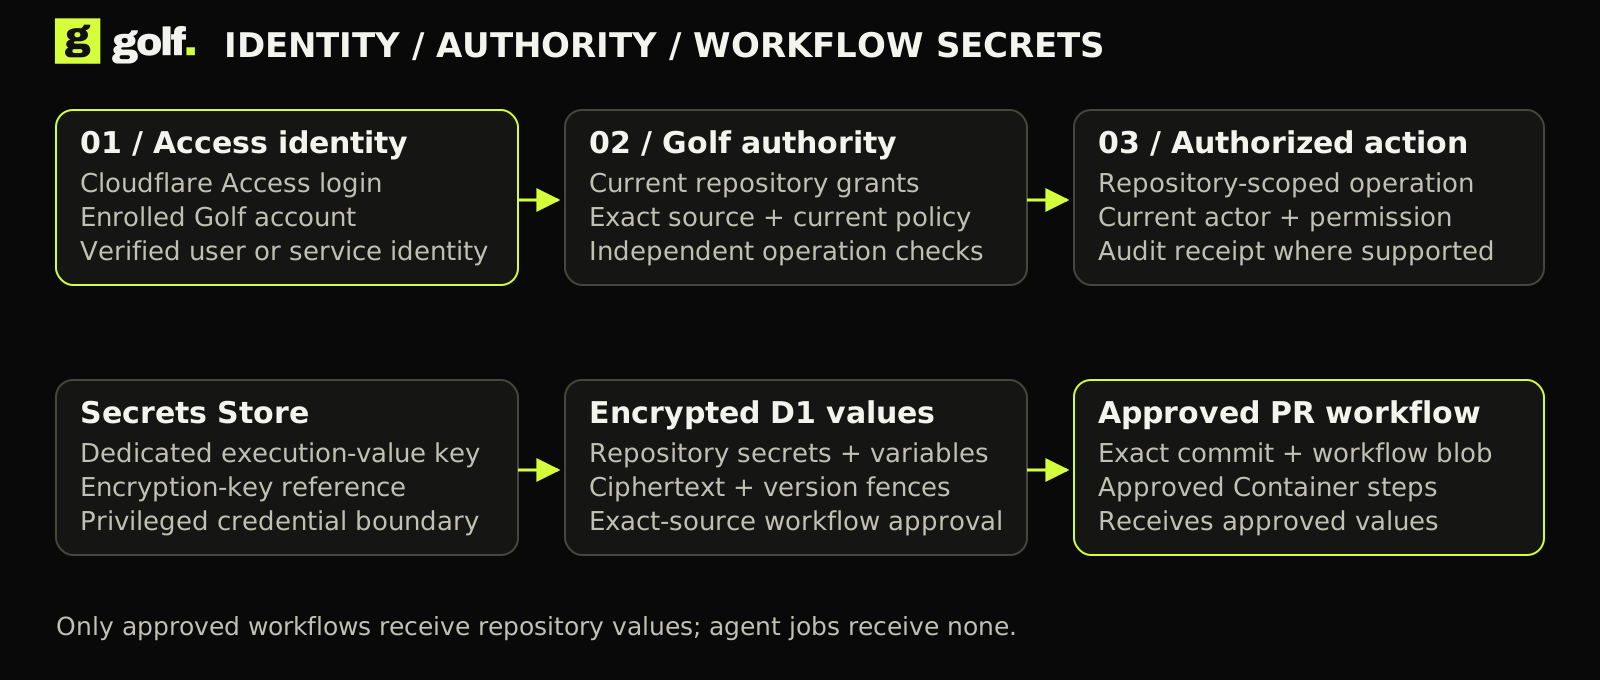
Access, Golf authority and deployment policy work together.
Separate human OTP and machine service admission; Golf requires an enrolled account and current grants.
Owned-zone control/preview hostnames and email sender records. Protection covers approved endpoints.
Encrypt repository values; approve exact-commit PR workflow release. Restrict preview branch, lifetime and concurrency.
Approximate anonymous read/clone throttling by network and location. Errors fail open; not a global quota.
Release secrets only to the approved exact-commit workflow.
Real messages retain consent, current access and delivery observations.
Own-address subscriptions and consent; sender subdomain and DNS onboarding. Retained provider acceptance is recorded.
Encrypted subscriptions, approved origins and stable event identity. A retained Slack test delivery was accepted.
Maintenance and bounded retries carry notification delivery. These consumers do not use the evidence queue.
Separate accepted notifications from maintenance and collection health.
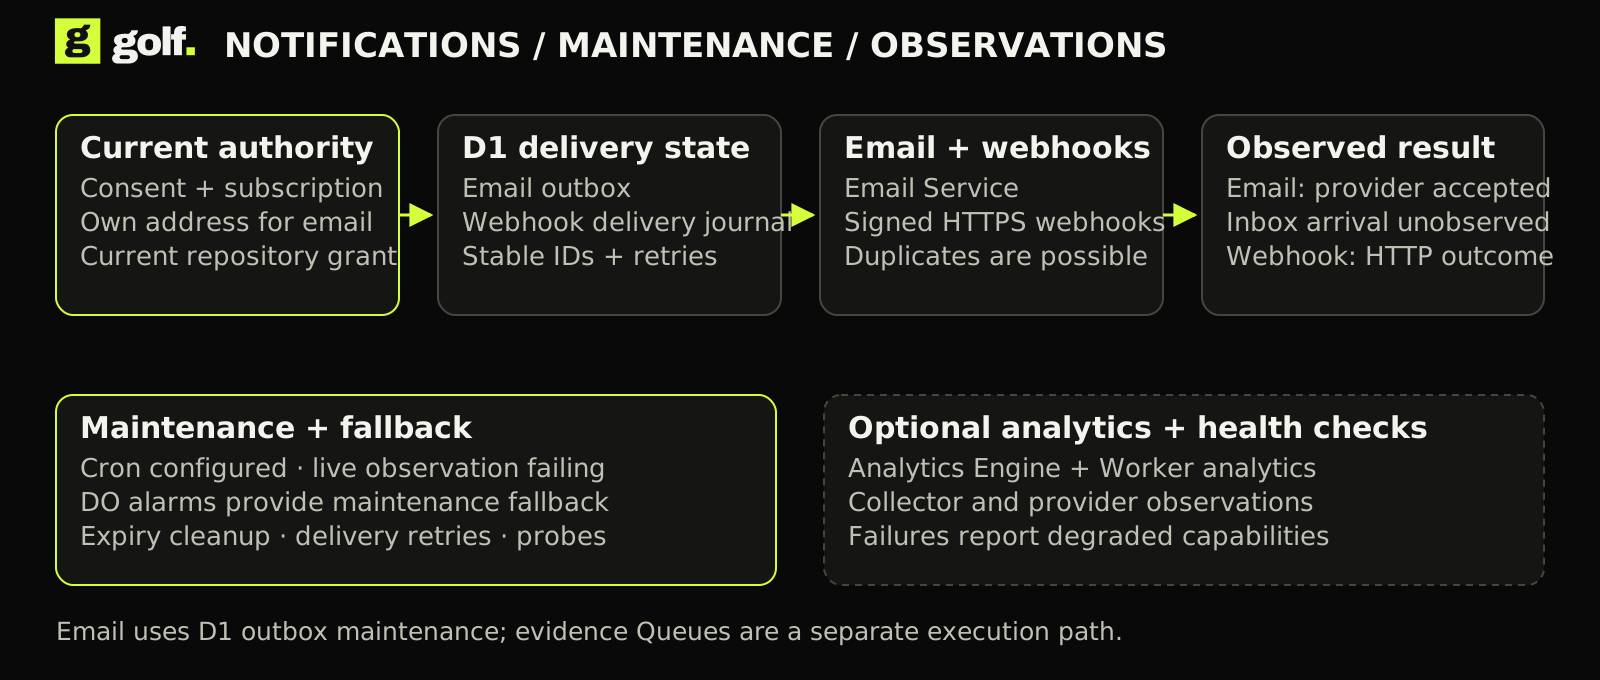
Infrastructure definitions and actual outcomes are separate evidence.
Bound optional evidence metrics; hosted ingestion/readback is not yet verified.
Separate read-only analytics token and enabled provider observations; analytics collection has recorded failures.
Cron schedule is configured but delivery is failing on this account. Workspace alarms have completed maintenance.
Owned resource provisioning, additive schema migration, token renewal, readback and cleanup.
Native standard merge has passed hosted Git checks.
Same-repository merge commit when the base is already an ancestor of head; verified ref/commit readback.
Squash, diverged branches, forks, drafts and locked targets are refused.
Complete trusted protected publication, broad merge semantics and general production promotion.
Semantic code and issue search is being added.
Create semantic representations from approved source content.
Index and query those representations to find related code and issues.
Filter results by live repository authority and propagate deletion/revocation.
Dated engineering proofs cover selected Git, test, proposal and protected-preview paths. Production readiness still needs testing.
Hosted Git, collaboration, approved tests, Clef advice, scoped proposals, protected previews, email acceptance and secret-to-step delivery.
Cron delivery and analytics collection; Analytics Engine ingest; retained screenshots; broader role/load/cleanup matrices.
Full parity, protected merge, production CD, native/Forgejo recovery, tenant onboarding and scale. Vectorize search is in development.
Start with a browser simulation, then install Golf to evaluate real workflows.
gitgolf.app/demo: explore local and Cloudflare interfaces with sample data. No backend or live execution.
Docker Compose or Golf’s Helm chart for portable hosting. Use the native Alchemy recipe in your own Cloudflare account.
Enroll a user and grant repository access on your installation. Check an exact commit and inspect its report. docs.gitgolf.app